About
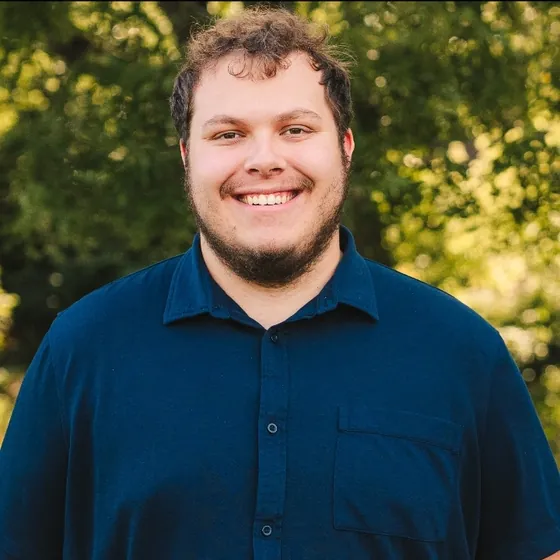
Hi, I'm Ethan.
I'm a cloud security analyst at a Fortune 500 insurer, where I work on GCP governance and security automation. At home I run my own infrastructure like production, and I attack it to see what holds.
I've always been the person who can't leave a problem alone. I chip away at it until it cracks, or it follows me around until it does. I was the one fixing the TV and the home internet, and I volunteered to film events at our town's yearly festival. CyberForce gave that habit a direction: keep a live network running while a red team tries to take it down.
Give me a task with clear instructions and it gets done to the letter: every detail checked, every decision backed by data. Give me an open problem and I start with where it breaks. Call it X-ray vision. When a plan comes up, I'm already mapping where it can go wrong and how to get around it before it does. In security, that habit has a name: threat modeling.
Now · November 2026
- Going deeper on Torq: building security automation workflows past the practitioner certification.
- Attacking every control in my homelab and publishing what held. the results →
- Rebuilding this site one page at a time, every number checked against a live source.
What I actually think
Anyone can assert these. So each one links to the place on this site where you can watch it hold.
- The guard has to be architectural, not textual. "Don't reveal X" in a prompt fails the first time someone is clever or insistent. The only defense that holds is an agent that doesn't possess the thing. Send it an injection and watch it have nothing to give up. try to break it →
- A control you have not attacked is a guess. Same for a backup that has never been restored. I test both and publish what happened, including what failed. see what testing caught →
- Prevention beats detection, and it is not close. A control that evaluates at creation has no exposure window to measure. Detection's best case still costs you the lag plus however long a human takes. run the timeline →
- Measure before you optimise, or you will spend the night on the wrong thing. I instrumented my voice assistant expecting text-to-speech to be the bottleneck. It was the fastest stage in the pipeline. see the numbers →
- Run what you build. I ship my own images of the recipe app my household actually eats from, so every regression I write lands on the machine I use at dinner. It is the fastest feedback loop I have. see the bug →
- Own the code, and "I wish it had X" becomes a thing you just do. Twenty-one releases of a manga reader later, that has been true every time. drive the reader →
Habits, not adjectives
- I attack my own controls before I trust them. A control counts once it has stopped something from outside, on the record. Four of mine failed that test the first time. see it →
- Detect, tune, then enforce. New controls start in audit or detection-only mode against real traffic. They move to blocking when the false positives are known, not before.
- Every risky change ships with its way back. Firewall rollouts go host by host with a ten-minute auto-revert armed. Updates keep a rollback image and a snapshot until the new version has run for a few days.
- Write it down while it happens. Changes, tests and decisions go into a dated log as I make them, so the next person, usually me, does not have to guess.
What I was wrong about
-
I thought My VPN isolation held because no other route existed.
Actually The route existed. What holds is a default-drop firewall in the namespace, and I trust it because I took the tunnel down six times and nothing got out. the proof →
-
I thought fail2ban was banning attackers at my edge.
Actually It logged bans and enforced none: the wrong firewall backend failed silently. Now no control counts until it has been tested from outside. the proof →
How I got here
- 2021
Electronics repair technician
Oct 2021 to Jul 2023 · Batteries Plus
- Diagnosed and repaired devices with visual, hands-on and computer-assisted testing.
- Wrote the estimates and work orders: parts, labor, and what was actually wrong.
-
First place, Lewis Cyber Flyer CTF
Capture the flag · Lewis University
- 2022
CyberForce: 5th of 160 teams
Department of Energy · defend a live network against a red team
- Also competed in the Collegiate Cyber Defense Competition (CCDC).
- 2023
Security advisor intern
Summer 2023 · Fortune 500 insurer
- Worked with security leadership to find and reduce risk.
- Owned a project on governing browser extensions across the company.
-
CyberForce again: 10th
Three weeks, hosted by Argonne National Laboratory
- Aimed higher than the year before. Our defenses held, and I came out much stronger at Active Directory hardening through group policy.
- 2024
B.S. Cybersecurity, Lewis University
4+1 program, straight into the master's
-
IT security rotational program, rotation 1: Security Remediation Management
Jun 2024 to Jan 2025
- Ran security risk remediation in ServiceNow GRC: tracking, routing each issue to an owner, and getting vulnerabilities closed on time.
- Co-built the cloud security request intake in ServiceNow, replacing ad-hoc email with structured, trackable requests.
- With vulnerability management, routed Wiz cloud misconfiguration findings into the ticketing system.
- 2025
Rotation 2: Cloud Security
Jan 2025 to Apr 2026
- Validated metadata for 1,100+ GCP projects and linked each one to its business application in the CMDB.
- Defined the container security operating model: a RACI across 46 controls, agreed with cloud engineering, networking and AppSec.
- Recommended GCP organization policy constraints that block risky configurations at the source, moving from fixing to preventing.
- Automated the weekly security metrics report: a multi-hour manual job now takes minutes.
-
M.S. Cybersecurity, plus two certifications
Google Cloud Digital Leader (Feb) · M.S. (May) · ISC2 CC (Jul)
- 2026
Cloud security analyst
Apr 2026 to now
- Assisted remediation management when unapproved pre-hardened container images were found: handled the ticket and saw it through to completion.
- Led a proof of concept of no-code SOAR platforms (Torq, Tines): workflows that enrich cloud vulnerability alerts automatically, demoed to leadership with an adoption roadmap.
- Wired Wiz findings into ServiceNow so tickets arrive with the asset owner and context already filled in.
-
At home: a homelab run like production
Torq Automation Practitioner (Aug) · and still building
- Every security control attacked from outside and the results published.
- A manga reader fork at 21 releases, and a fix merged into Mealie.
The rest of it
PADI certified diver. My favorite book series is Brandon Sanderson's Reckoners, starting with Steelheart. I also read a lot of manga and manhwa, mostly long action series, which is why Makimono exists: an itch to fix the reader I use every day. On the shelf right now:
- Steelheart
- Return of the Blossoming Blade
- Nano Machine
- Revenge of the Baskerville Bloodhound
- SSS-Class Revival Hunter
- Nebula's Civilization
On paper, briefly
- Education
- M.S. Cybersecurity, Lewis University, 2025
- B.S. Cybersecurity, Lewis University, 2024 (4+1 program)
- Certifications
- Google Cloud Digital Leader
- ISC2 Certified in Cybersecurity (CC)
- Torq Automation Practitioner
- PADI certified diver
Web version: no phone number, no street address.
Where to find me
justice.ethan04@gmail.com · LinkedIn · GitHub · security.txt
More